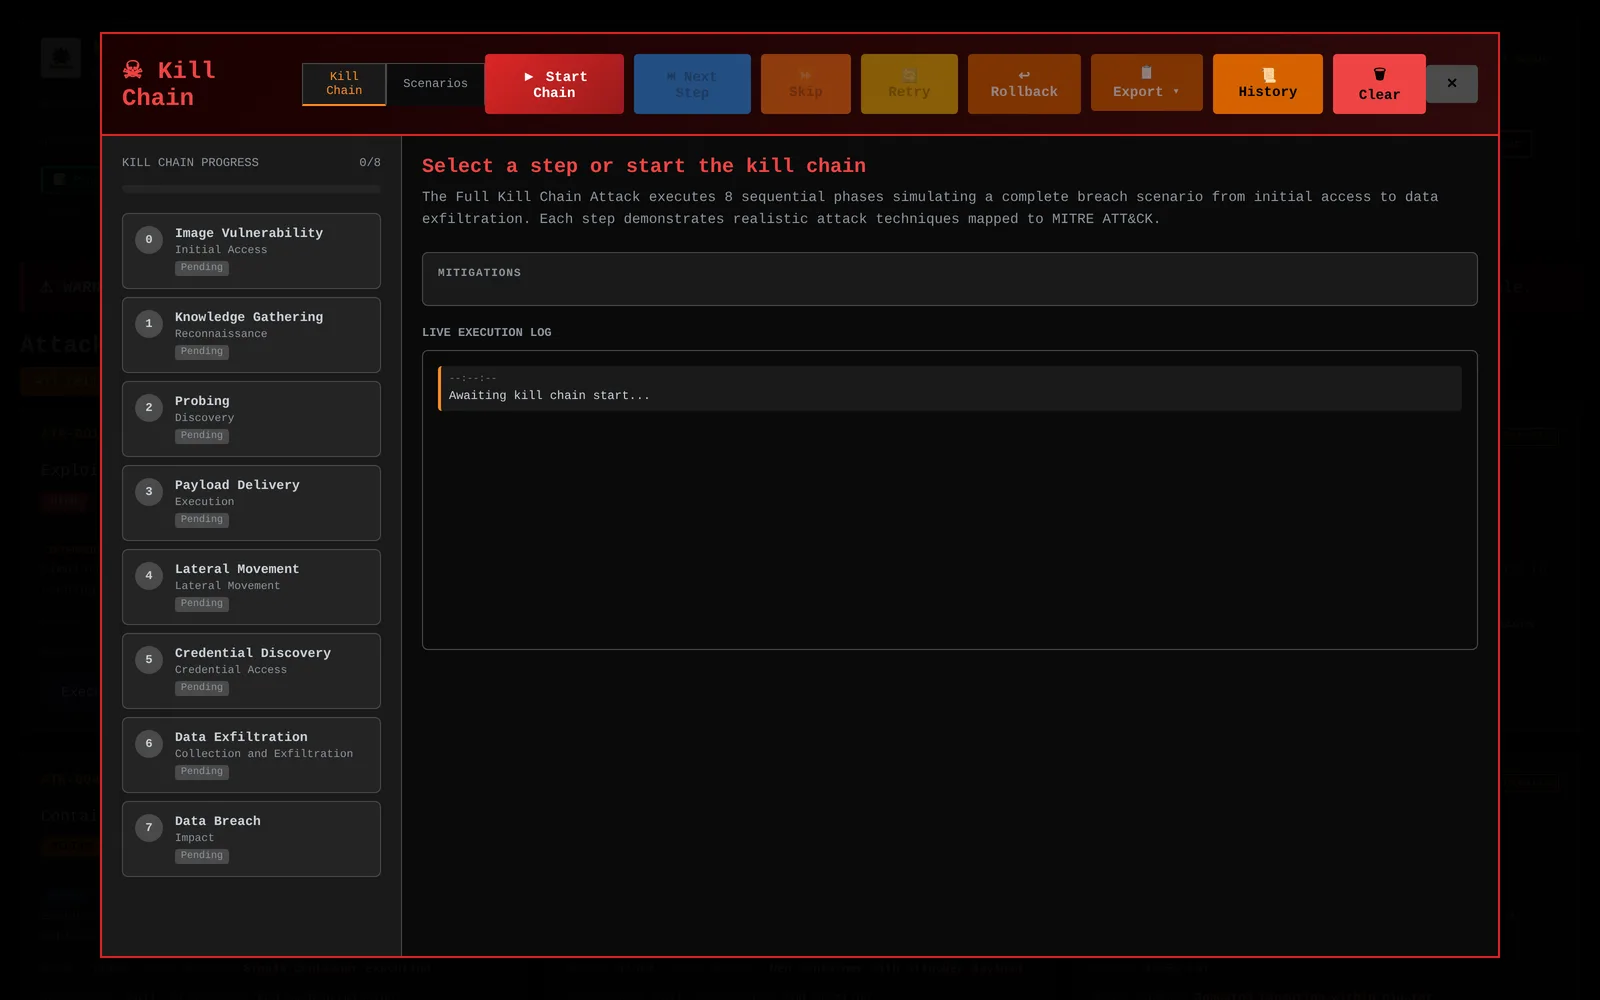
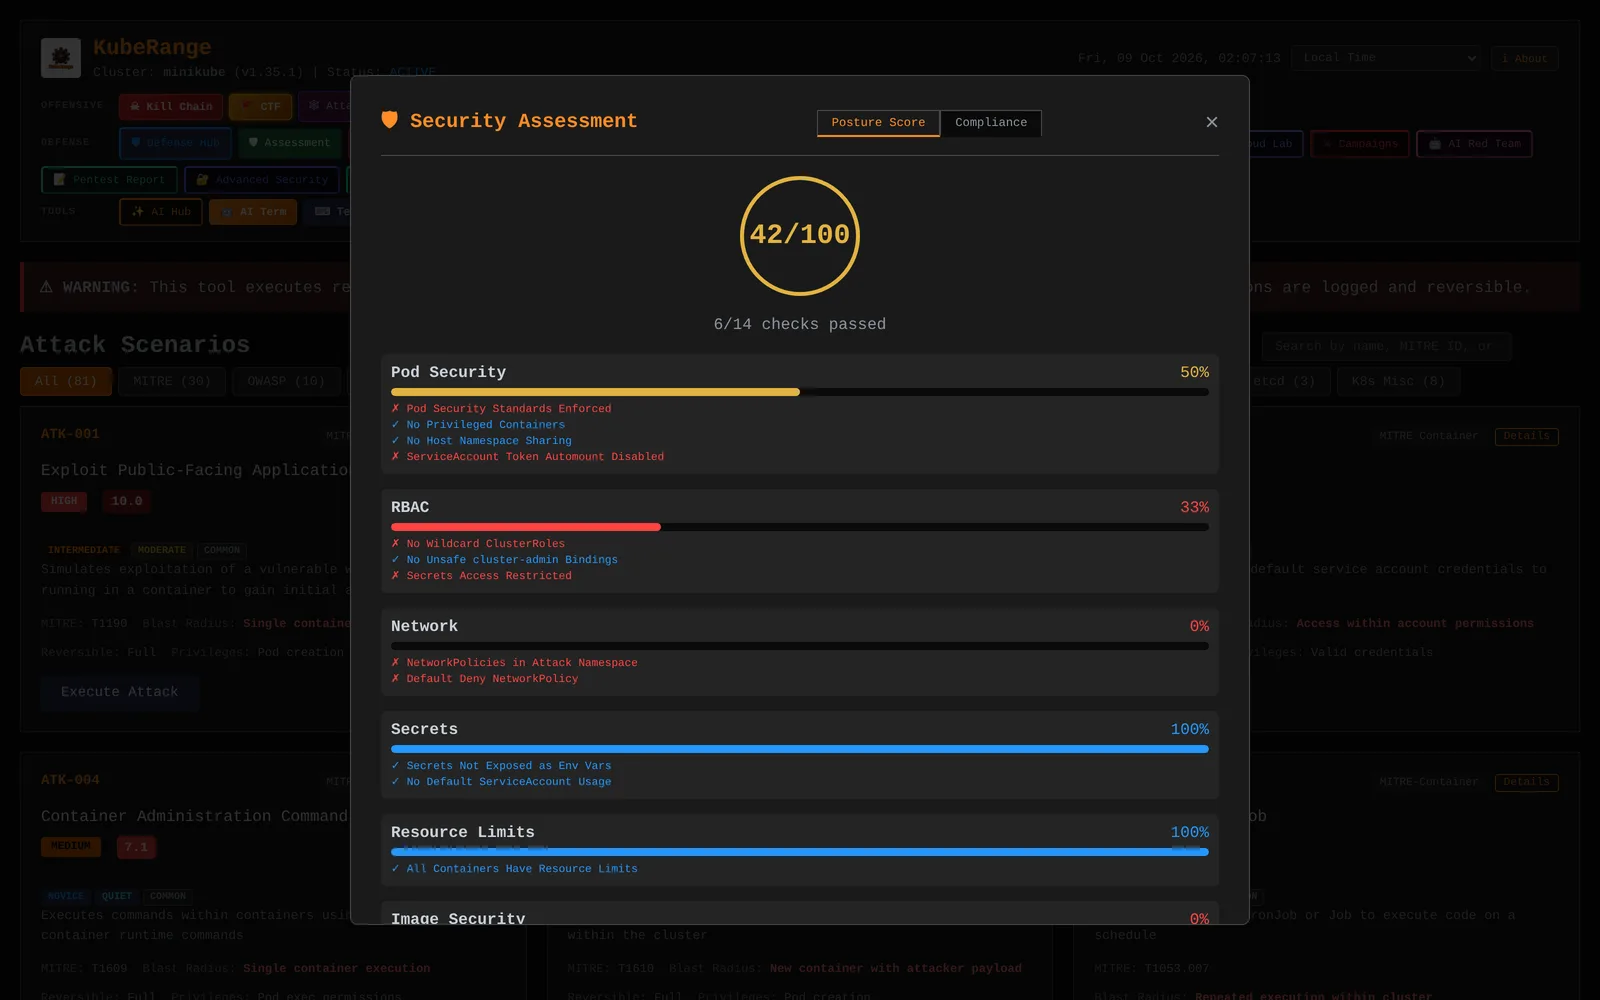
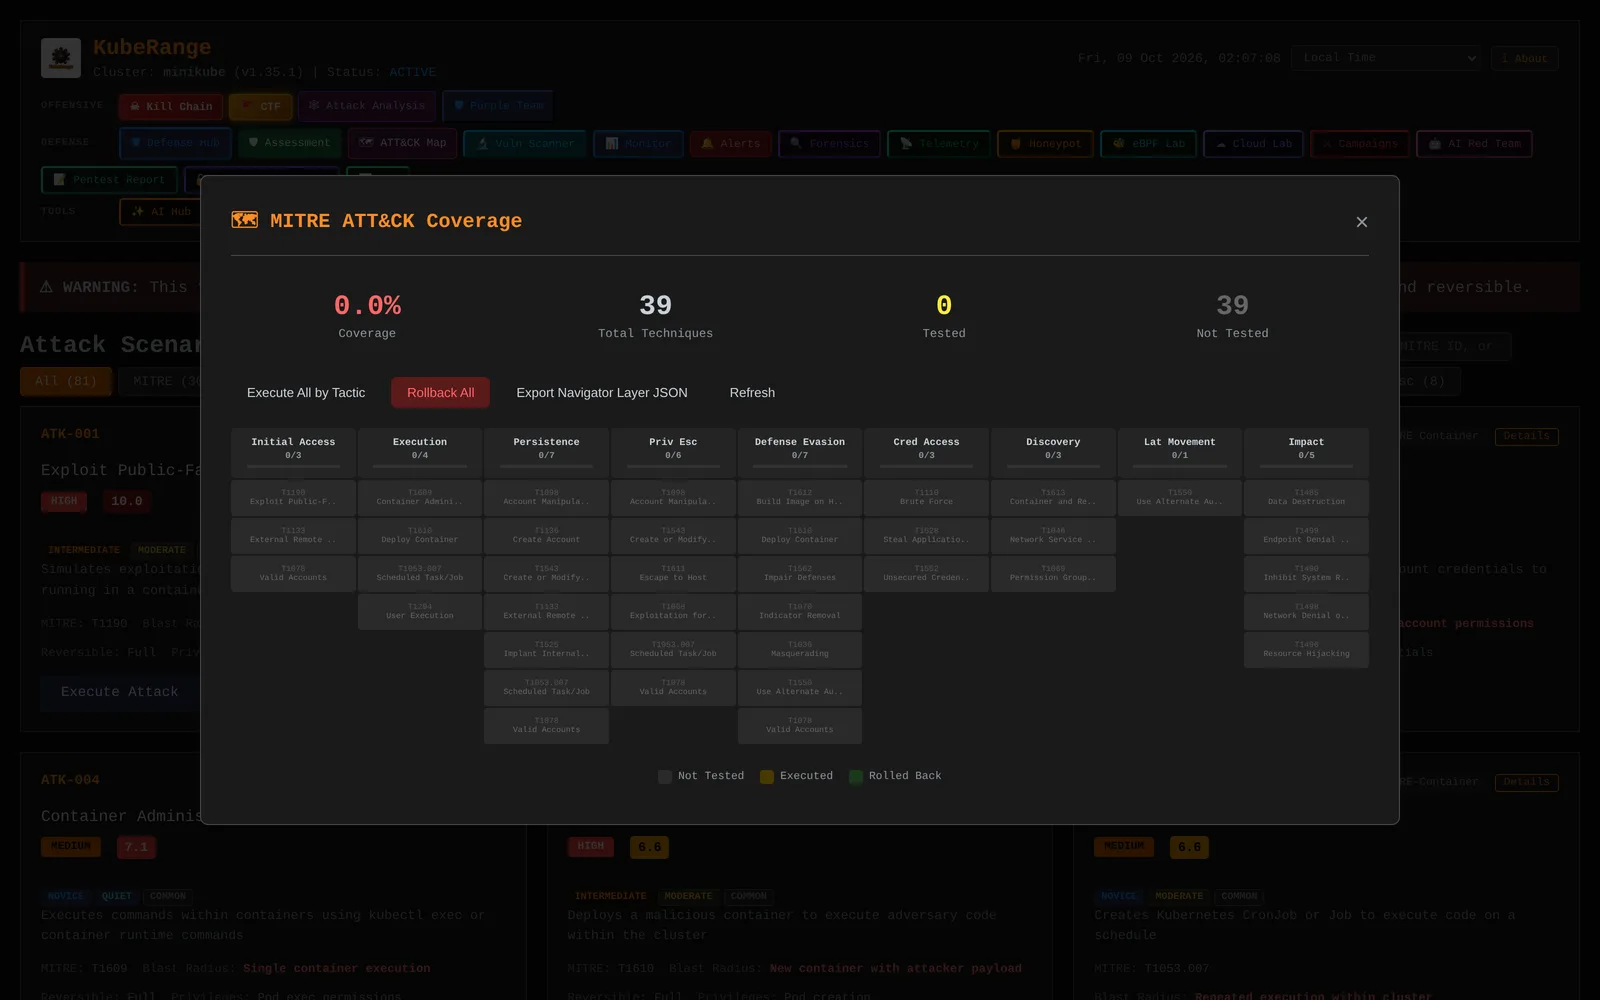
A Kubernetes cyber range in one Go binary. Run 83+ realistic attack scenarios inside a throwaway cluster, study what changed, and undo every change with one click.
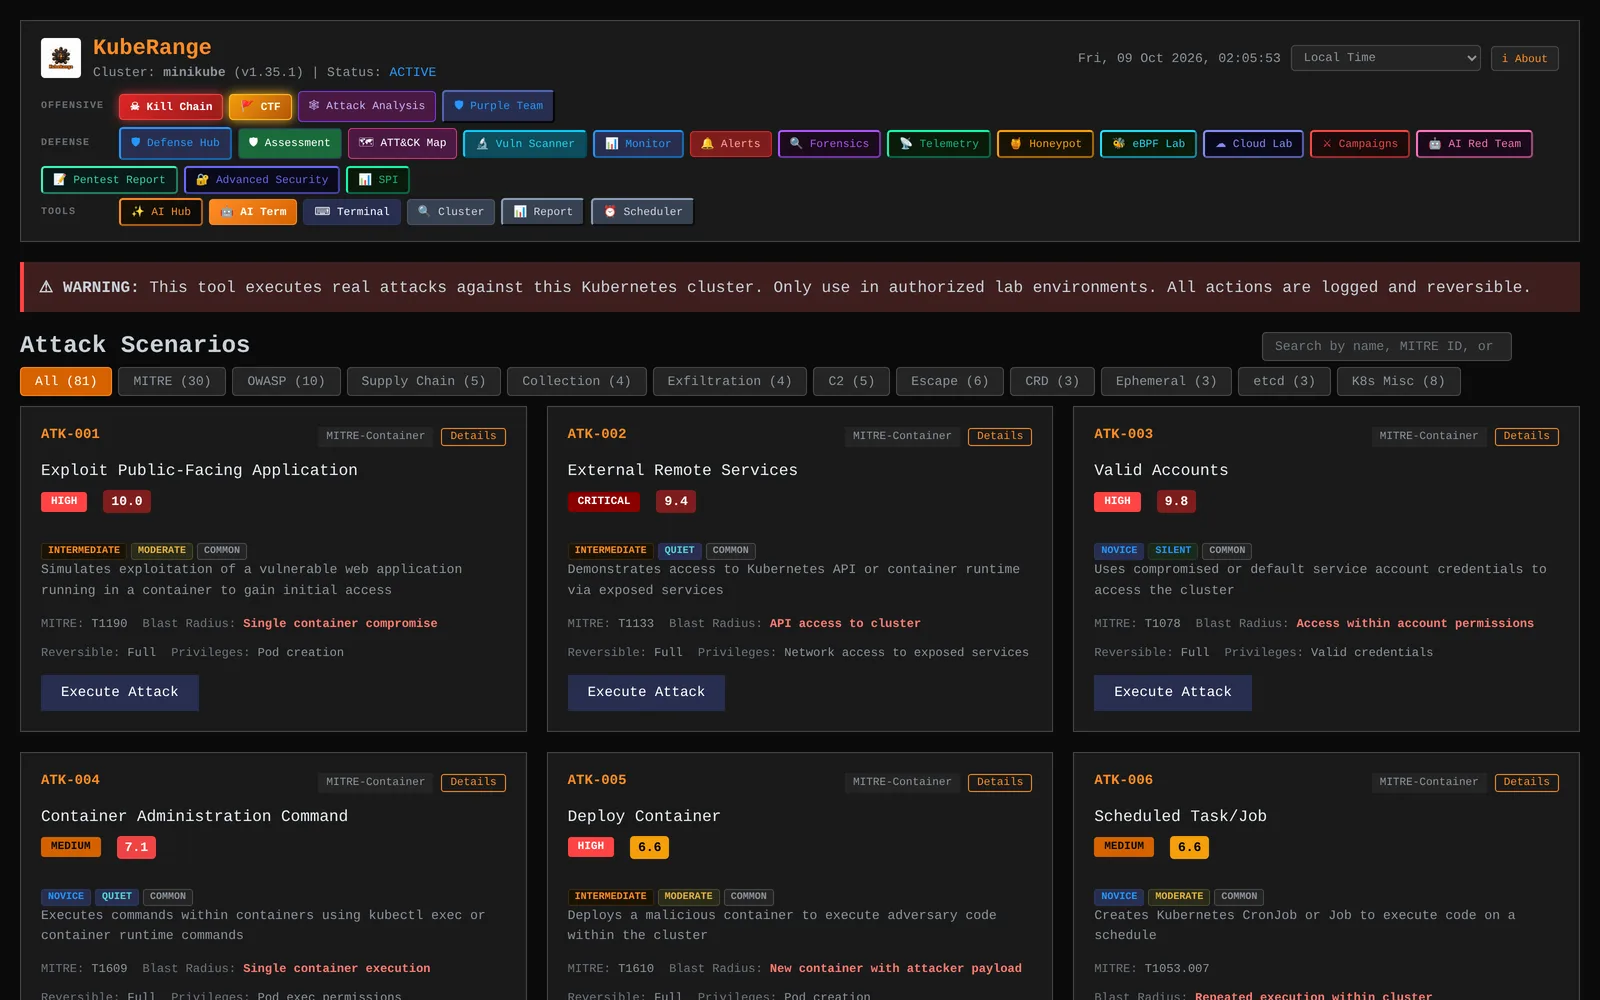
Each created, modified or host-level change is tracked in SQLite before it happens. Rollback is idempotent and safe to repeat, so a lab cluster can be attacked, studied and returned to a clean state.
Organized against the MITRE ATT&CK container matrix and the OWASP Kubernetes Top 10.
Every change is journaled in SQLite, so undoing an attack is idempotent and repeatable.
Zero-trust network-policy synthesis, RBAC remediation, policy diffing and chaos tests alongside the attacks.
Vulnerability scanning plus a runtime monitor for processes, files and network flows.
See which techniques have been exercised, chain them into kill chains and review the timeline.
A live PTY terminal in the single-page dashboard, served by the same Go binary.